A new EU rulebook is coming
The European Union’s new anti-money laundering framework is one of the biggest compliance changes coming to iGaming. Regulation (EU) 2024/1624 applies from 10 July 2027, and it replaces much of the existing directive-based approach with rules that apply directly across member states. For operators used to national variations, that is a significant change.
A directly applicable regulation matters because it removes some of the room for interpretation that came with a directive. Each member state has transposed directives into national law in its own way, which produced differences in timing and detail. A regulation applies in the same form everywhere in the bloc, so operators will have fewer local variations to manage.
The new supervisory body is taking shape
The EU’s new Anti-Money Laundering Authority, known as AMLA, has begun consulting on its rules. In March 2026 it opened consultations on three draft regulatory acts. These will shape how the authority supervises high-risk sectors, and gambling is among the sectors operators should watch closely.
Consultation stages matter because they are the point at which the industry can push for practical rules. Operators that submit comments early can influence the detail, while those who wait may find themselves working within requirements they did not shape.
Enforcement is already visible
The new rulebook is not the only pressure. Enforcement against KYC and AML failures is already happening. Curaçao has fined 12 operators over KYC failures in a recent settlement, a signal that licence holders in that jurisdiction face real consequences for weak controls. It shows regulators are willing to act, not only to publish guidance.
Fines in iGaming are rising in many places. One 2026 commentary argues that regulators have built specialist enforcement teams and now expect operators to show their controls work, rather than simply state that the controls exist. That is a useful way to think about the standard: evidence matters more than policy documents.
Brazil’s banking deadline
Brazil offers a useful example of how financial institutions are being drawn into the fight against illegal betting. Central Bank Resolution BCB 569/2026 requires institutions to share fraud data linked to unlicensed operators. For certain transactions tied to illegal virtual asset services, the required measures must be adopted by 30 October 2026.
That matters for iGaming operators even outside Brazil. Payment and banking partners are increasingly expected to identify and report suspicious flows, which means operators need to be able to explain their own flows clearly and quickly.
What a practical KYC programme looks like
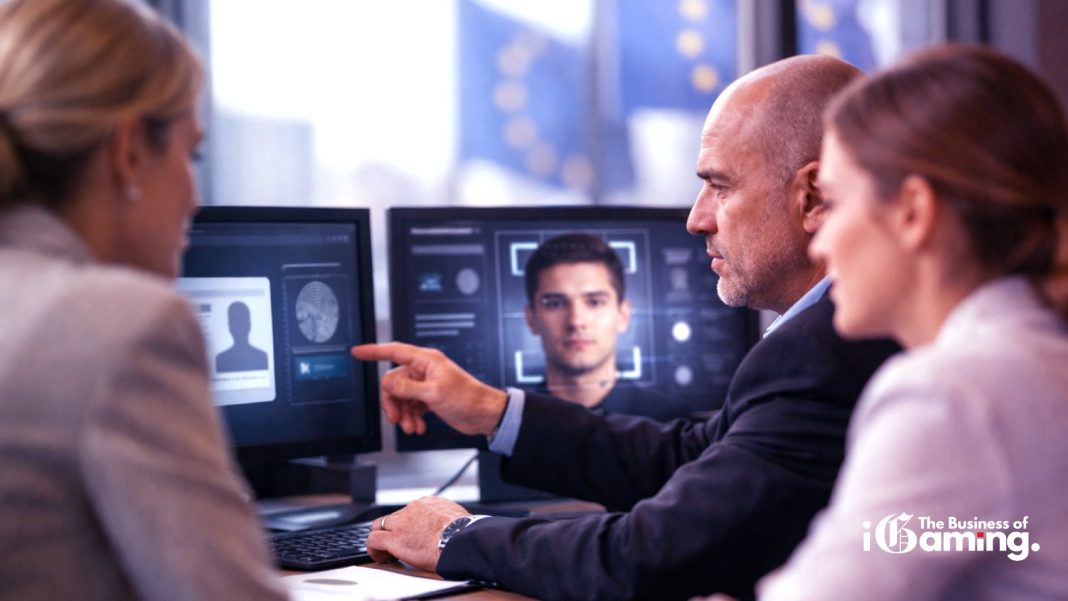
Good KYC programmes are built in layers rather than as a single onboarding step. A practical structure usually covers identity verification, address checks and, where the risk requires it, evidence of the source of funds. Ongoing monitoring then picks up changes in behaviour after the player is onboarded.
Technology helps, but it does not replace judgement. Automated tools can flag mismatches and speed up checks, while compliance staff still need to review escalations and decide what to do with them. Operators who treat automation as a complete answer tend to find gaps in their audit trail.
- Map each market you serve against its specific identity and AML requirements.
- Verify identity, address and source of funds at the risk levels that apply.
- Monitor transactions and player behaviour after onboarding, not only at sign-up.
- Keep records of decisions so you can show regulators how the controls worked.
Documentation and the audit trail
When a regulator reviews an operator, the first question is often not whether a control exists but whether it was applied consistently and recorded at the time. That makes the audit trail as important as the control itself. Operators should be able to show when a check was run, what data it used, what result it produced and who reviewed any escalation.
Policies should be dated and version-controlled. A policy that was updated after an incident, or after a change in law, should show what changed and why. Regulators are more forgiving of a process that improved over time than of one that looks like it was written to satisfy a single inspection.
Training records belong in the same file. Staff who handle onboarding, payments and escalations need documented training, refreshed when rules change. A control that depends on one trained person is fragile, and it is one of the first things an examiner will test.
Preparing for the 2027 date
The EU framework applies from July 2027, which leaves time for a structured plan. A sensible first step is a gap analysis that compares current procedures against the new requirements, market by market. The gaps that matter most are usually in identity verification standards, the depth of source-of-funds checks and the way suspicious activity is escalated and reported.
The second step is to test the changes rather than only document them. Run a sample of recent player files through the revised process and see how many need additional work. That exercise shows where the real effort will fall, and it gives leadership a realistic budget and timeline.
The third step is to keep a close eye on the consultations. Regulatory technical standards often change the detail that operators care about most, and early engagement through industry bodies can help shape practical outcomes.
Common gaps found in reviews
Certain weaknesses come up again and again in compliance reviews. The first is inconsistent identity checks, where the same player is verified to one standard at sign-up and to a lower standard at withdrawal. The second is source-of-funds checks that are triggered by a threshold but never revisited when a player’s behaviour changes. The third is escalation paths that exist on paper but are not used, because staff are unsure who makes the decision.
Another common gap is poor vendor oversight. Many operators rely on third-party KYC and monitoring providers, but they do not test those providers’ accuracy or review their results regularly. A provider that performs well at onboarding may still miss problems later, and the operator remains responsible for the outcome.
Finally, reviews often find that the compliance function is not given enough access to commercial data. If the team responsible for AML cannot see deposit patterns, affiliate sources or bonus usage, it cannot spot the links that matter. Closing that gap is often cheaper than the fine that follows a missed pattern.
Our analysis
One possible reading of the current pattern is that regulators are moving from rules to proof. The old question was whether an operator had a policy. The new question is whether that policy works and whether there is evidence to show it. The enforcement examples suggest, though do not confirm, that this shift will accelerate once the EU framework applies.
Final thoughts
The EU anti-money laundering rules will not apply until July 2027, but operators who prepare now will have far fewer surprises. The current enforcement climate, from Curaçao to Brazil’s banking rules, shows that the cost of getting controls wrong is already rising.
Follow Business of iGaming for updates on AML and KYC developments across Europe and beyond, and get in touch if you want to talk through how new rules might affect your compliance plans.